
During the last part decade, the Emotet malware has emerged as a best Web danger that pillages other folks’s financial institution accounts and installs different varieties of malware. The sophistication of its code base and its incessantly evolving strategies for tricking goals into clicking on malicious hyperlinks—in September, for example, it all started a unsolicited mail run that addresses recipients by way of title and quotes previous emails they despatched or gained—has allowed it to unfold broadly. Now, Emotet is adopting but differently to unfold: the usage of already compromised units to contaminate units attached to within reach Wi-Fi networks.
Ultimate month, Emotet operators had been stuck the usage of an up to date model that makes use of inflamed units to enumerate all within reach Wi-Fi networks. It makes use of a programming interface known as wlanAPI to profile the SSID, sign energy, and use of WPA or different encryption strategies for password-protecting get right of entry to. Then, the malware makes use of certainly one of two password lists to wager usually used default username and password combos.
After effectively having access to a brand new Wi-Fi community, the inflamed instrument enumerates all non-hidden units which are attached to it. The usage of a 2d password checklist, the malware then tries to wager credentials for every person attached to the force. Within the match no attached customers are inflamed, the malware tries to wager the password for the administrator of the shared useful resource.
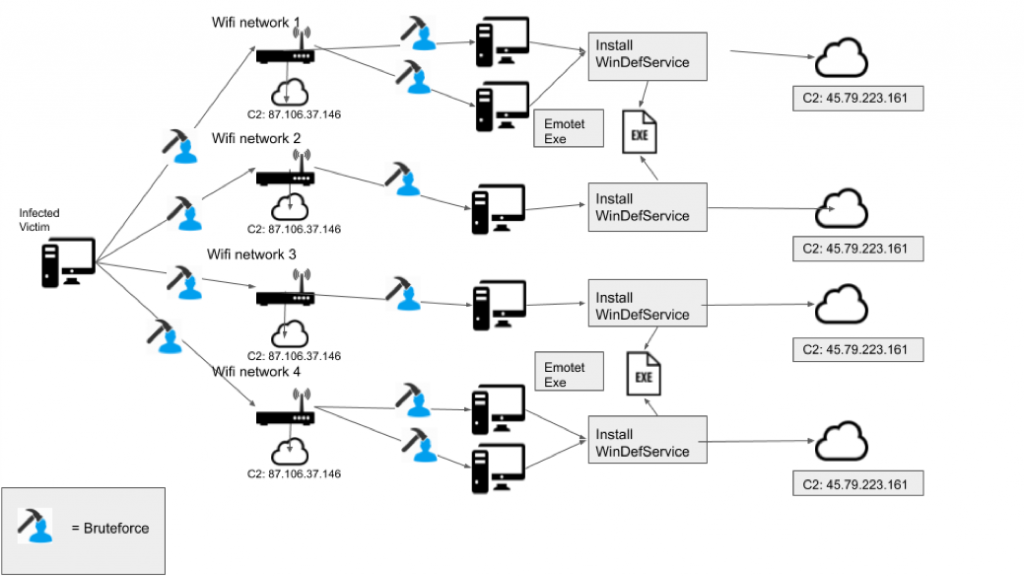
Whilst Emotet is highest recognized for circulating via malicious electronic mail runs, it has additionally been seen spreading in worm-like style from instrument to instrument over inflamed networks. Within the match it effectively guesses the password to a attached instrument, it then quite a bit the Emotet malware and perhaps different items of malware—such because the Ryuk ransomware or the TrickBot malware—in alternate for charges paid by way of operators of the ones campaigns. Not content material with infecting handiest units within the compromised community, Emotet is now the usage of the newly found out model to leap from community to community.
Watch out for susceptible passwords
“With this newly found out loader-type utilized by Emotet, a brand new danger vector is offered to Emotet’s functions,” researchers from safety company Binary Protection wrote in a lately revealed put up. “Prior to now concept to simply unfold via malspam and inflamed networks, Emotet can use this loader-type to unfold via within reach wi-fi networks if the networks use insecure passwords.”
The Binary Protection put up stated the brand new Wi-Fi spreader has a timestamp of April 2018 and used to be first submitted to the VirusTotal malware seek engine a month later. Whilst the module used to be created virtually two years in the past, Binary Protection didn’t apply it getting used within the wild till ultimate month.
The newly documented spreader underscores the significance of the usage of robust passwords to limit get right of entry to to Wi-Fi networks. Emotet’s up to now recognized skill to unfold from instrument to instrument inside a community already underscored the significance of the usage of robust passwords to limit get right of entry to to units attached to native networks. Passwords must at all times be randomly generated and must by no means be fewer than 11 characters.
One facet of the brand new Wi-Fi spreader is out of maintaining with Emotet’s same old penchant for stealth of class. The module makes use of unencrypted connections to be in contact with attacker-controlled servers. That makes it simple to stumble on patterns in site visitors that folks can use to stumble on infections. The malware will also be detected via lively tracking of attached units for brand new services and products being put in and staring at for any processes or services and products working from brief information and person profile utility information folders. The Binary Protection put up supplies different signs of compromise.


